Legit or Phishing Trap? Visual Proof Behind the Viral Youtube Verification Text Phenomenon
 By James H. Sterling
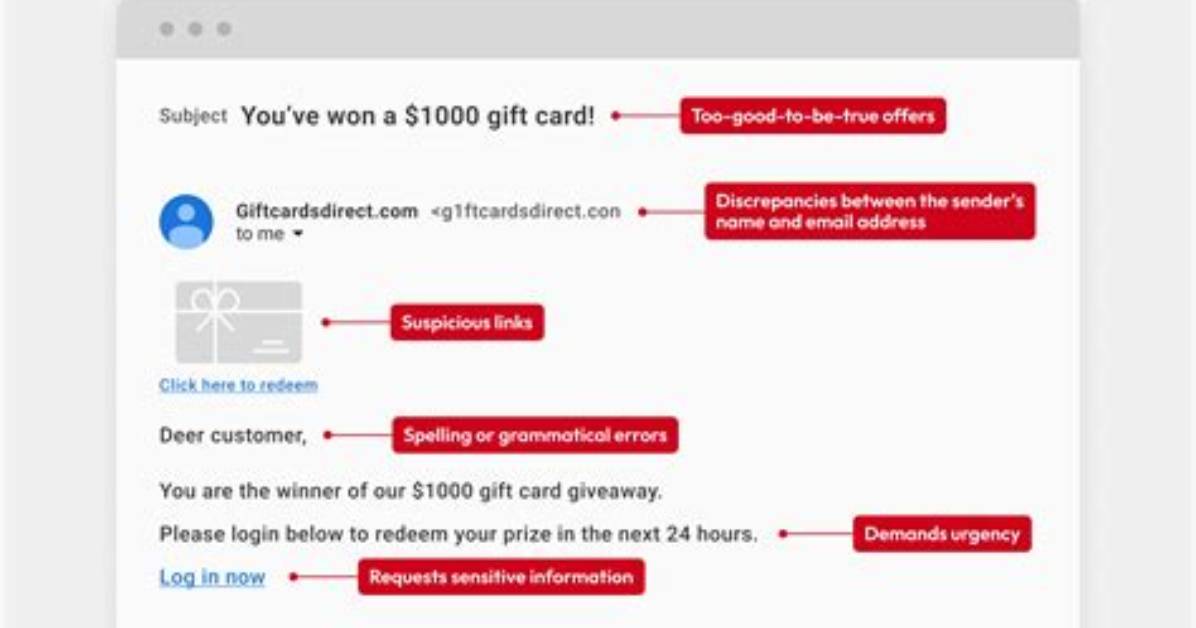
Relying on mobile text messaging for authentication is no longer adequate for channels with commercial value. Telecommunications infrastructure has proven too susceptible to smishing manipulation, SIM swapping, and interception attacks. Hardening an enterprise or personal YouTube account requires eliminating reliance on SMS authentication altogether.
Moving away from SMS begins with configuring FIDO2-compliant physical hardware keys, such as a YubiKey or Titan Security Key. Hardware tokens communicate directly with the web browser using origin-bound cryptographic proofs. If a user inserts a hardware key on a fraudulent URL like `g-verify-sync[.]net`, the key evaluates the origin URL, identifies the domain mismatch, and refuses to sign the authentication request. The session token cannot be stolen because no data is transmitted.
For creators who cannot deploy physical hardware keys across their teams, software-based authenticator apps like Google Authenticator, Aegis, or 1Password provide an alternative that decouples codes from SMS delivery. In these applications, the Time-based One-Time Password (TOTP) algorithm runs locally on the device without transmitting requests across telecommunications lines. Crucially, creators must remember an absolute rule of the platform: Google will never provide a third-party link or external web portal requiring a user to calculate, verify, or sync an existing one-time password.
James Sterling reports on renewable energy developments, climate policy, ecological conservation, and green tech innovations around the globe.
